Explore the Catalog

Tutorials, challenges, courses, skill paths, playgrounds, and more — search the whole library in one place.

Tutorial

Native SSH Reverse Tunneling with Pomerium

Use Pomerium's native SSH support to publish a local service through a standard reverse SSH tunnel, with OpenID Connect (OIDC) authentication and continuous authorization on every request. Reach services behind Network Address Translation (NAT) without firewall holes or custom agents, and control both who can use the service and who can open the tunnel. Application traffic stays on infrastructure you control.

Native SSH Reverse Tunneling with Pomerium (cover image)
Tutorial

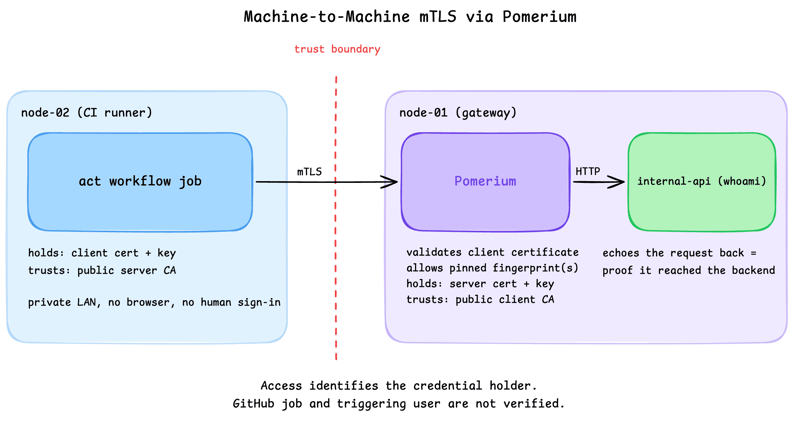
Secure Machine-to-Machine Access with mTLS and Pomerium

Run a GitHub Actions-compatible continuous integration (CI) job on a private runner and protect its internal API call with mutual TLS (mTLS) and Pomerium. Build separate server and client trust chains, authorize one machine certificate by fingerprint, then revoke, restore, and rotate its credentials through live policy changes.

Secure Machine-to-Machine Access with mTLS and Pomerium (cover image)
Tutorial

Harden Access to OpenClaw with Pomerium

Put OpenClaw, a self-hosted AI assistant with shell and file access, behind a web route and an SSH route, both gated by the same identity and Pomerium's context-aware policy. OpenClaw runs in trusted-proxy mode, trusting signed identity headers instead of its own login, while Pomerium's native SSH proxy signs short-lived certificates for shell access.

Harden Access to OpenClaw with Pomerium (cover image)
See all tutorials →
Challenge

Reach a Linux Service Through an Interface It Doesn't Listen On

On a dual-homed Linux server, a service bound to the IP address of one interface may still accept connections that arrive through the other interface. Learn how to reach such a service through an interface it doesn't listen on, using a routing trick.

Challenge

Harden a Django GraphQL API: Five Classic Flaws

A stock Django + Strawberry GraphQL service ships with five common weaknesses. Probe each one from the terminal, fix it in the real project, and watch the lab confirm the remediation against the live endpoint.

Challenge

Intercept and Analyze Encrypted Traffic of a Suspicious Container

Play a security researcher: identify the hosts a black-box container keeps making encrypted HTTPS calls to, route them through a MITM proxy, fake the certificate, and see what the container sends over the network.

See all challenges →
Course
Work-in-Progress

Hands-On Firecracker: microVMs From First Principles to Production

A hands-on introduction to Firecracker that takes you from booting your first microVM to building secure, production-ready sandbox infrastructure. Learn how to launch and control microVMs, wire up networking, share data efficiently, and harden execution - the essential skills for running autonomous agents and untrusted workloads safely at scale.

Hands-On Firecracker: microVMs From First Principles to Production (cover image)
Course

Kubescape Nodeagent Dungeon

A detailed walkthrough of Kubescape Nodeagent, observing a fileless (pseudo) attack all the way from the Kernel to the Alert.

Kubescape Nodeagent Dungeon (cover image)
Course

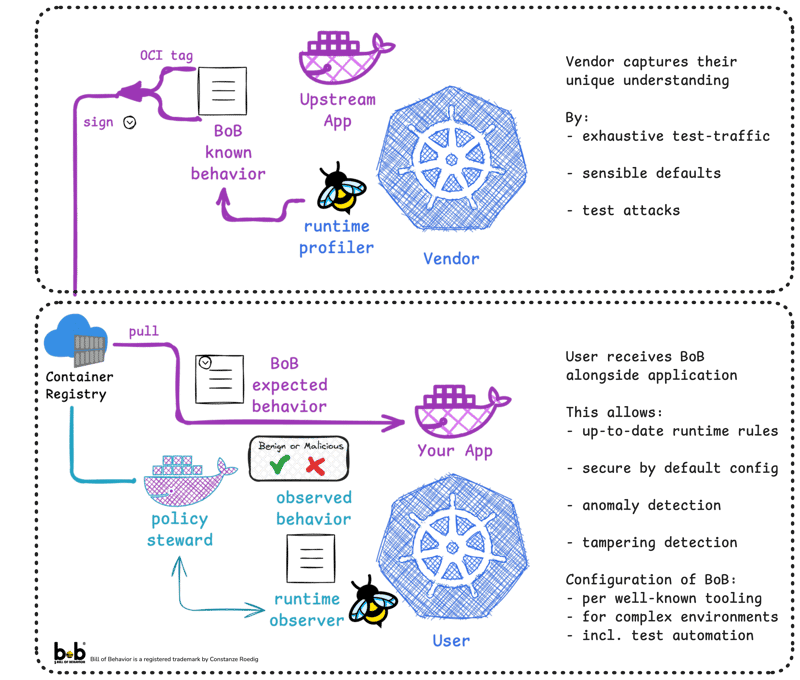
Software Bill of Behavior - vendor supplied runtime profile for tampering and anomaly detection

We ♥️ supply chain security, thus was created SBOM - the Bill of Materials- but, we also need SBOB -the Bill of Behavior - This livelab proposes to standardize how to record a benign behavior profile, extract, sign and publish it, for users to consume, ingest, verify it and detect attacks and tampering. For software-vendors, a SBOB creates trust and transparency, For users, it makes anomaly detection realistically achievable.

Software Bill of Behavior - vendor supplied runtime profile for tampering and anomaly detection (cover image)
See all courses →
See all skill paths →
Playground on  Linux, Security

Kali Linux

Kali Linux - for all sorts of information security testing.

Playground on  Observability, Security

Tetragon

A 3-in-1 playground (Kubernetes, Docker, and vanilla Linux hosts) to experiment with Tetragon - an eBPF-powered security observability tool.

Playground on  Containers, Security

minT(oolkit)

Don't change anything in your container image and minify it by up to 30x making it secure, too!

Playground on  Kubernetes, Containers, Security

OpenClaw on K3s with agent-sandbox + gVisor

A 3-node K3s cluster with gVisor (runsc), the kubernetes-sigs/agent-sandbox controllers, and the OpenClaw + gVisor example pre-deployed. OpenClaw's Control UI is available as a dedicated tab.

See all playgrounds →