eBPF Tracepoints, Kprobes, or Fprobes: Which One Should You Choose?
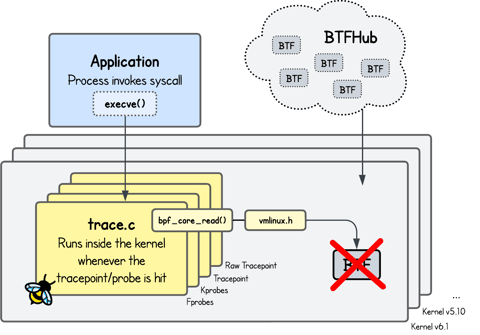
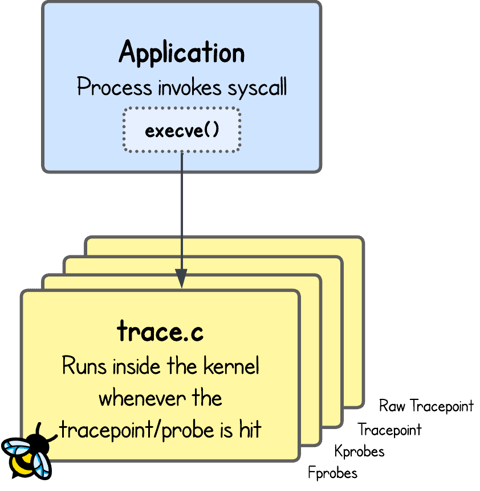
In this tutorial, we’ll look at how different eBPF tracing mechanisms work in practice by focusing on a single use case: capturing execve system call events. We’ll start with tracepoints, move on to raw tracepoints, and then cover kprobes and fprobes, showing how each attaches to the kernel and what data they expose. Along the way, we’ll compare their trade-offs in terms of stability, performance, and portability.