Tutorial on ,
MCP Fundamentals: OAuth 2.1 Auth and Security

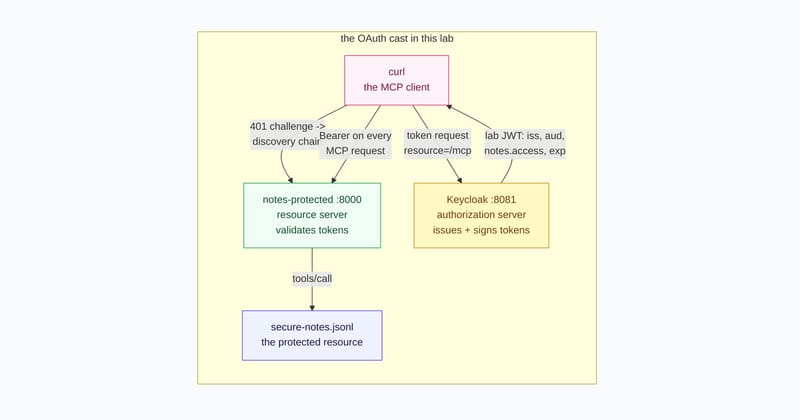
Protect an HTTP MCP server with MCP's OAuth profile and a real Keycloak authorization server. Follow the 401 challenge and discovery chain with curl, mint an audience-bound token, and use it in a Bearer-protected MCP session. Then test a wrong-audience token and study token passthrough, confused-deputy, DNS-rebinding, and tool-poisoning attacks.