
eBPF and WASM - Better Together
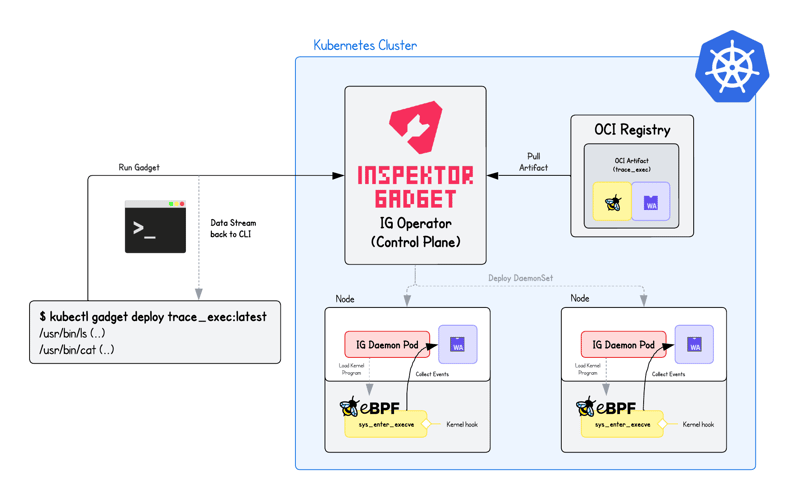
Learn how Inspektor Gadget pairs eBPF with WASM to process kernel events—and walk through the same idea yourself by implementing a minimal example.
Tutorials, challenges, courses, skill paths, playgrounds, and more — search the whole library in one place.
Learn how Inspektor Gadget pairs eBPF with WASM to process kernel events—and walk through the same idea yourself by implementing a minimal example.
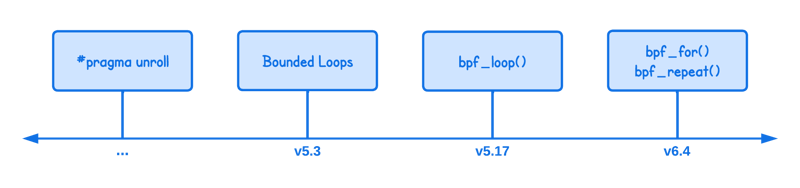
In this tutorial you will learn different ways to implement loops in eBPF, explaining how iteration evolved from manual loop unrolling to modern mechanisms like bounded loops, helper functions, and open-coded iterators. It walks through the limitations, kernel version requirements, and practical examples for each approach so you can choose the most appropriate looping method for your eBPF programs.
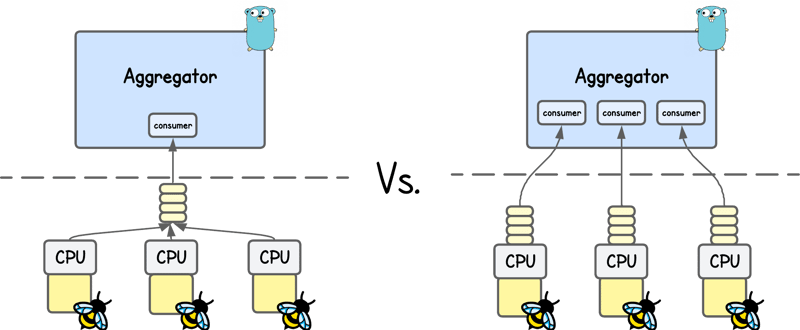
In this tutorial, you’ll learn how eBPF applications send kernel events into user space using perf buffer and ring buffer, exploring their design, trade-offs, and performance implications. You’ll also learn how moderns solutions like Jibril handle high-throughput event delivery.
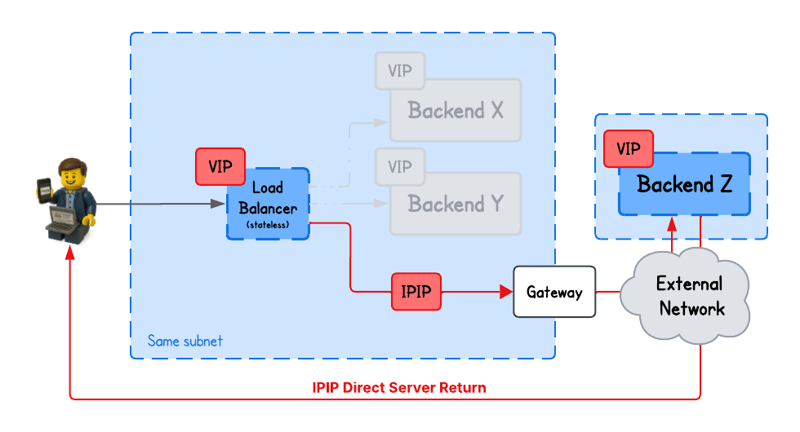
In this tutorial, you will learn how to build a IPIP DSR load balancer using eBPF/XDP, where backends from arbitrary networks send responses directly back to clients bypassing the load balancer.
In this challenge, you’ll debug and fix a deliberately “broken” eBPF program, then prove it’s running by identifying its program and map IDs. Along the way, you’ll explore bpftool, check which helpers are supported, and dig into details like the UID of the loader. Finally, you’ll test your knowledge of eBPF maps by recalling the flag that only inserts a key if it doesn’t already exist.
A hands-on learning path that teaches how to use eBPF and XDP for high-performance, in-kernel packet processing, from protocol parsing to advanced use cases like firewalling, rate limiting, and load balancing.
In this learning path, you’ll go from comparing different tracing program types — tracepoints, raw tracepoints, kprobes, and fprobes — to writing portable eBPF programs that work reliably across environments. You’ll also understand the role of BTF and learn how to make your eBPF code portable even when BTF isn’t available on the target system.
Learn eBPF from the ground up — from writing and running your first program, to storing data in eBPF maps, inspecting and monitoring kernel activity using bpftool and bpftop, and understanding how the verifier ensures safe eBPF execution. Finish with a hands-on challenge to put your new skills to the test.