Course
Software Bill of Behavior - vendor supplied runtime profile for tampering and anomaly detection

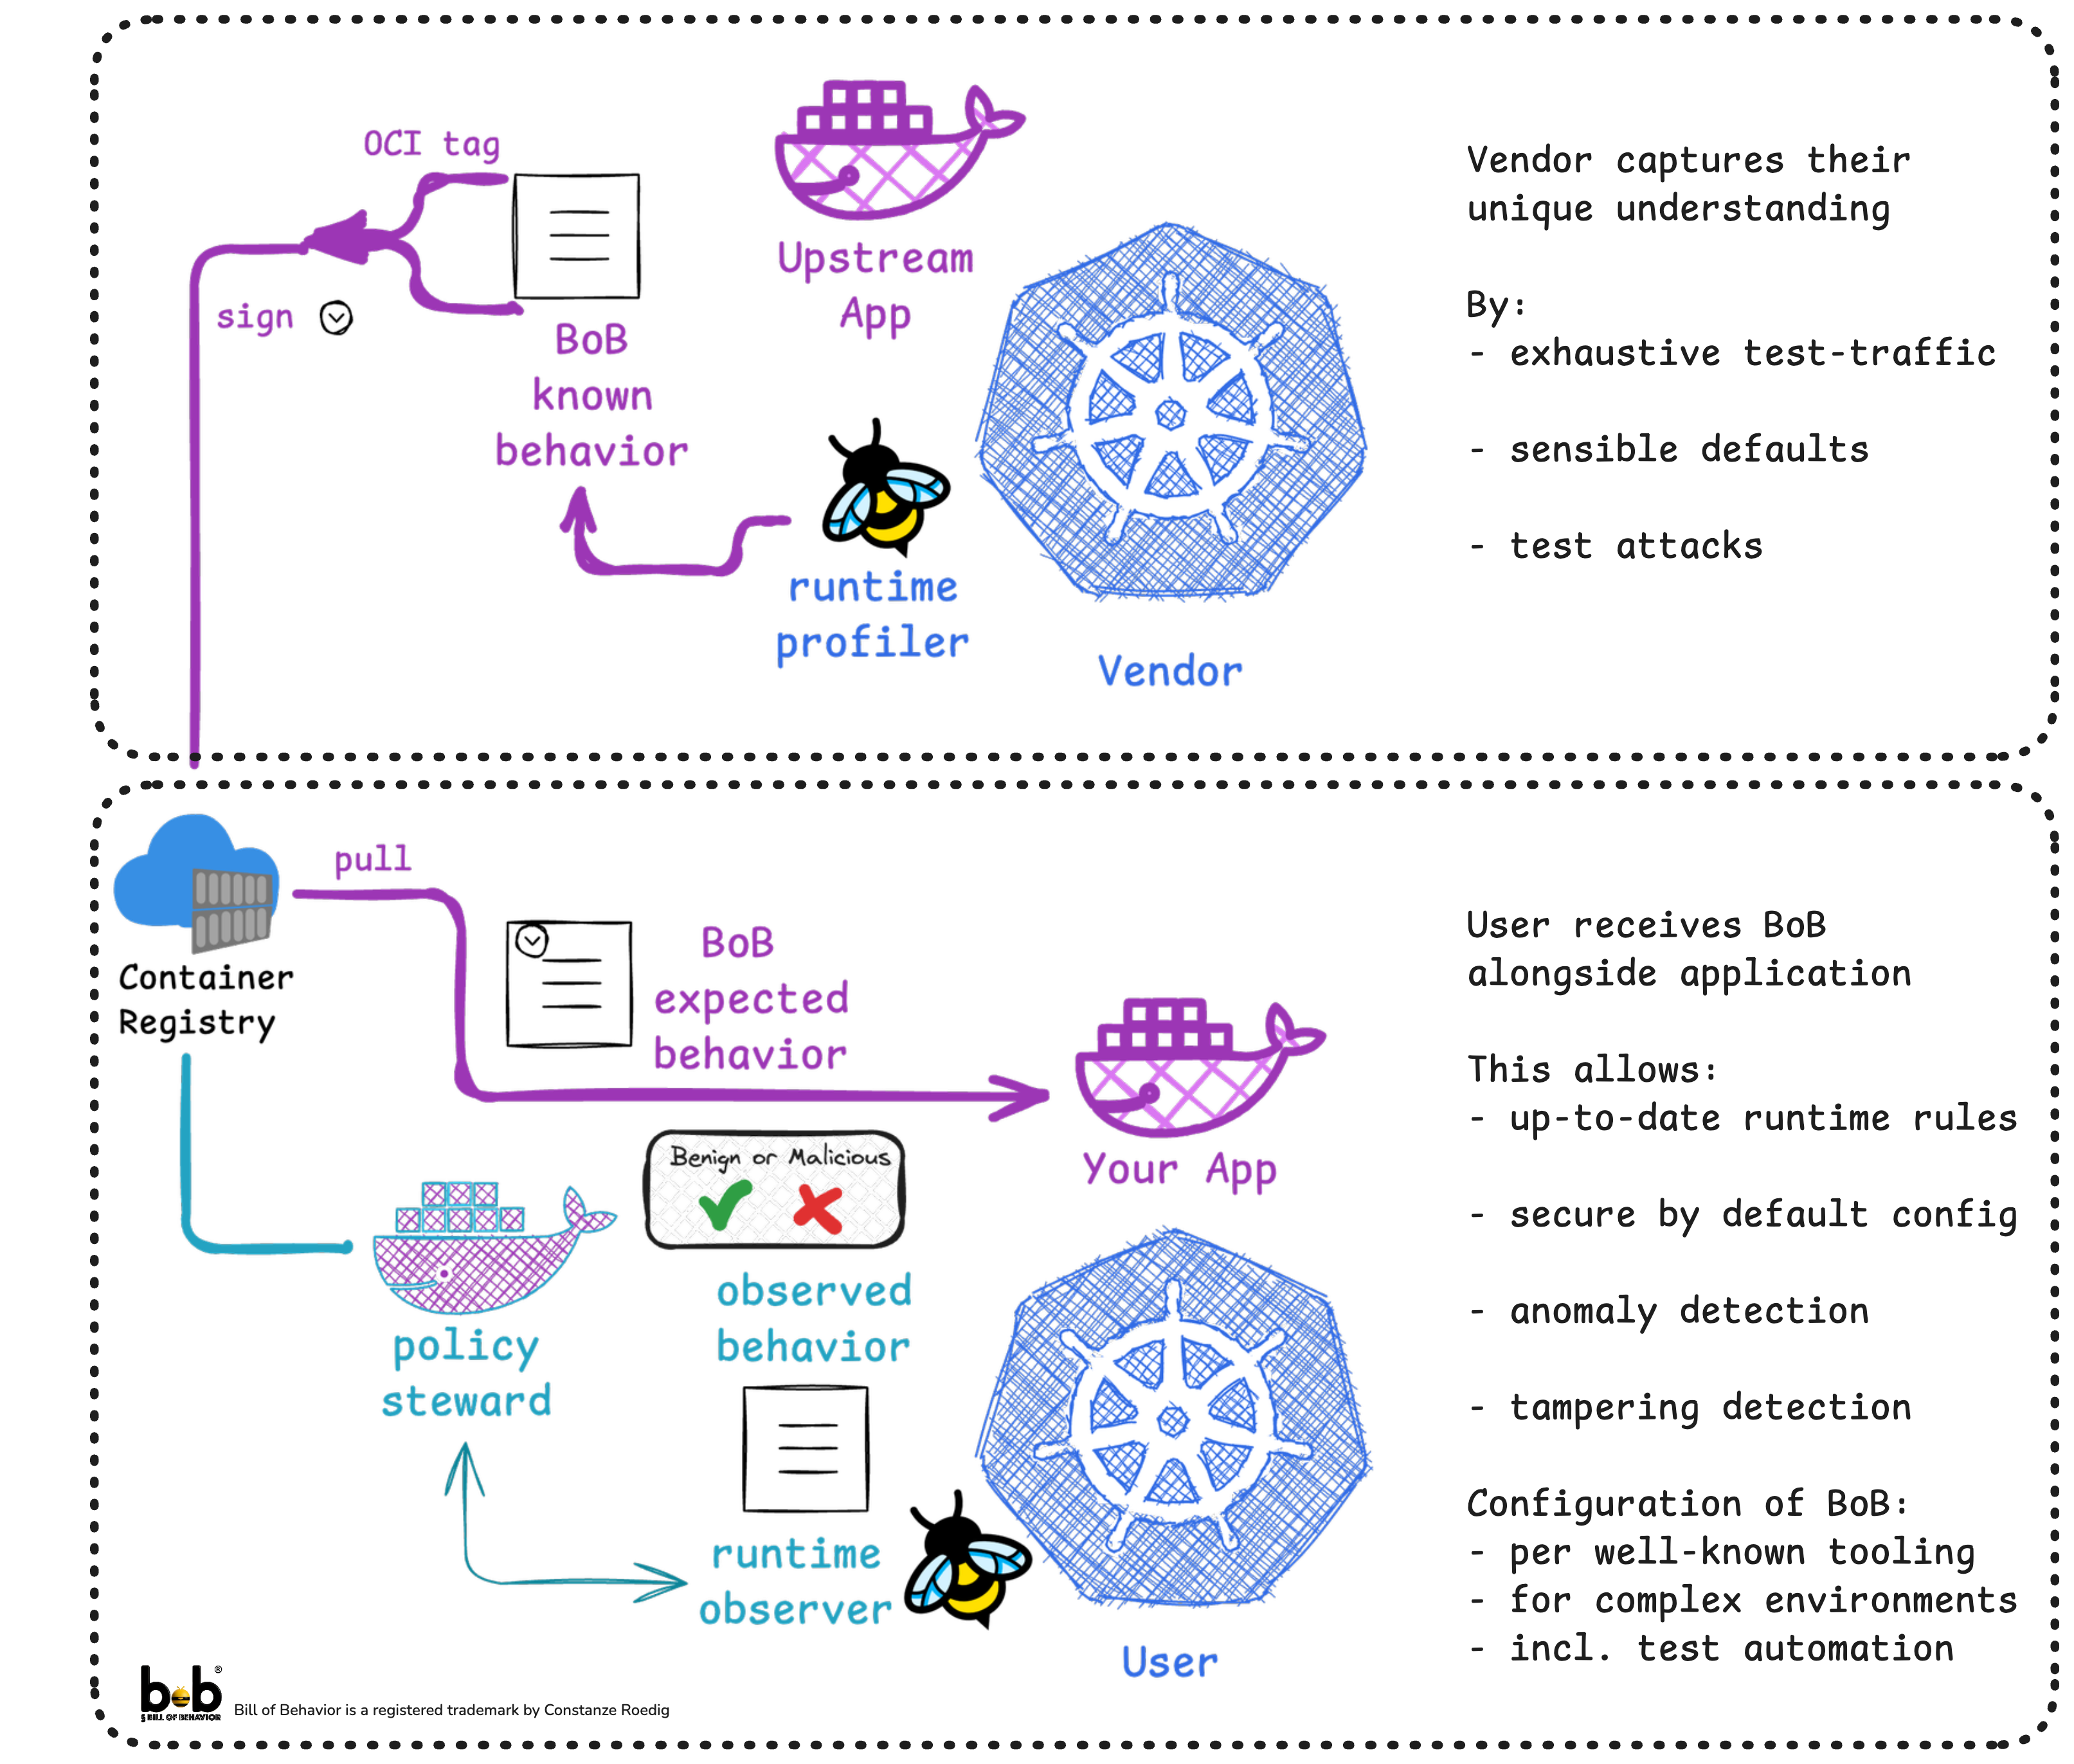
We ♥️ supply chain security, thus was created SBOM - the Bill of Materials- but, we also need SBOB -the Bill of Behavior - This livelab proposes to standardize how to record a benign behavior profile, extract, sign and publish it, for users to consume, ingest, verify it and detect attacks and tampering. For software-vendors, a SBOB creates trust and transparency, For users, it makes anomaly detection realistically achievable.
About This Course
We ❤ security, but what do you do when you cannot scan ?
For this, (zero-days, stolen or leaked credentials or agents gone off the rails) comes the Software Bill of Behavior, we lovingly call it BOB...
🚨Yes, this lab is finally back, completely reworked and with the latest Kubescape features in it. We'll add more examples and features as they become GA.
You can contribute to the bobctl repo under the Kubernetes Stormcenter or check out the progress of the initiative under billofbehavior.com
What's Inside?
About the author
Writes about
Frequently covers