Course on ,
Workload Identity from Scratch: Re-Inventing SPIFFE with OpenSSL, MariaDB, SoftHSM2, and a TPM

by med unes
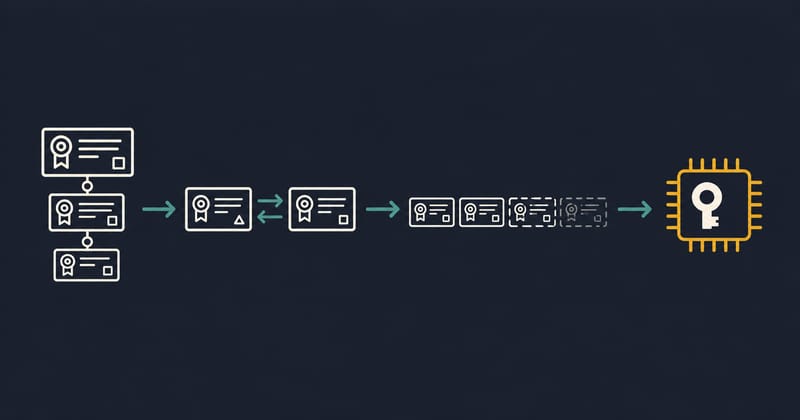
Services authenticate to each other with shared secrets that leak, never rotate, and cannot prove who is really calling. Here we build the alternative by hand: we verify a server the way a browser does, add mutual TLS bound to a specific identity, make certificates short-lived so a stolen one is worthless, then bootstrap it all with attestation and hardware-rooted keys. It is the model behind SPIFFE, built from openssl, MariaDB, SoftHSM2, and a TPM.