Set Up Network Address Translation (NAT) for a Container

Premium Challenge
Upgrade your membership to unlock this and all other premium materials.
There is an improvised "container" implemented with a network namespace.
You can see it in the ip netns list output.
The container is connected to the host with a veth pair and can ping the host's end of it (172.18.0.1),
but it cannot call any other addresses.
Your task is to connect the container to the outside world.
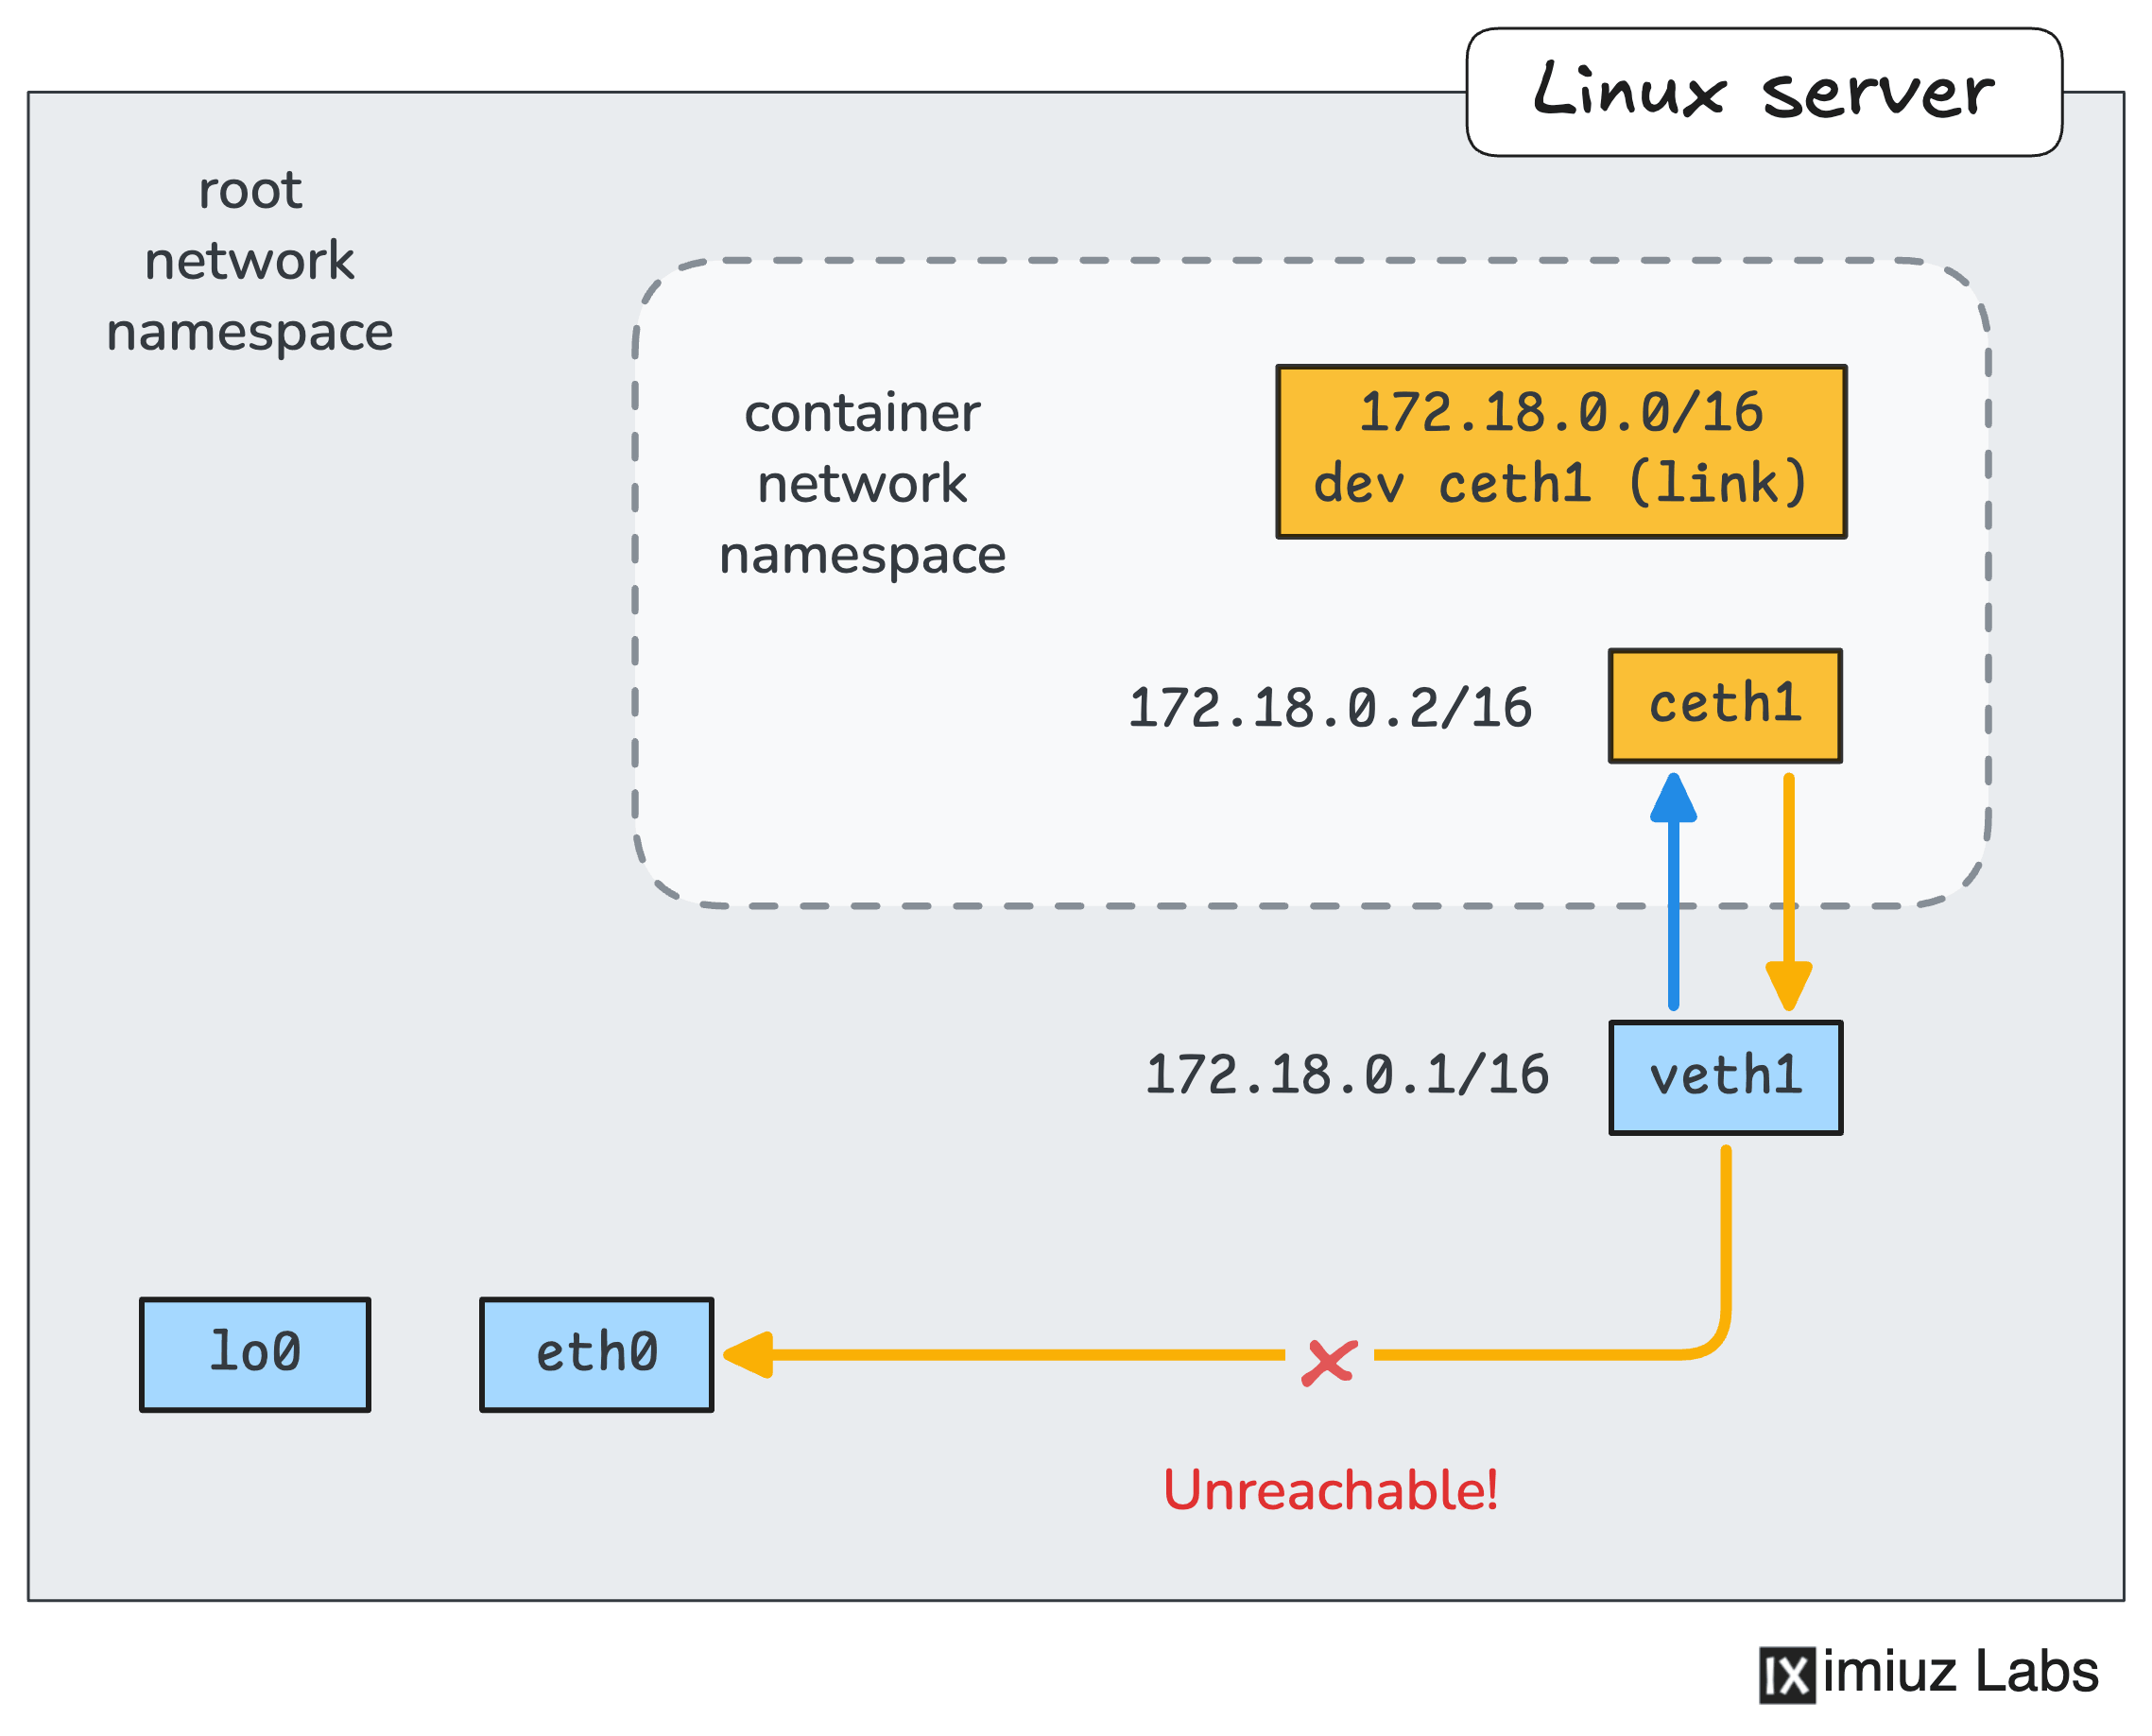
First, make the container reach the host's eth0 interface:
Hint 1
The container is already connected to the host's network namespace via its veth pair, so the missing part must be something else.
Check the container's routing table.
Is there a route for destinations outside the 172.18.0.0/16 network?
Then, make the container reach the Internet:
Hint 2
When a packet destined for the Internet leaves the container, it has the source IP address set to the container's IP.
This address is local to the host,
and the Internet destination simply wouldn't know how to reply to it because there are billions of 172.18.0.2 devices out there.
Hint 3
You need to replace the source IP address of the packet with the host's IP address before it leaves the host. This technique is known as Source Network Address Translation (sNAT).
Hint 4
Still feeling lost? The keywords are iptables and MASQUERADE.
Hint 5
Added a masquerade rule but the container still cannot ping the Internet? Make sure the host is configured to forward packets between interfaces. By default, it's usually not.